Platform · IxProve
Continuous compliance monitoring and evidencing
Continuous compliance monitoring and evidencing.
Posture per framework is computed from the live decision ledger, each control shows what is evaluated, enforced and drifting, and evidence packs export on demand. The audit is done before anyone asks.
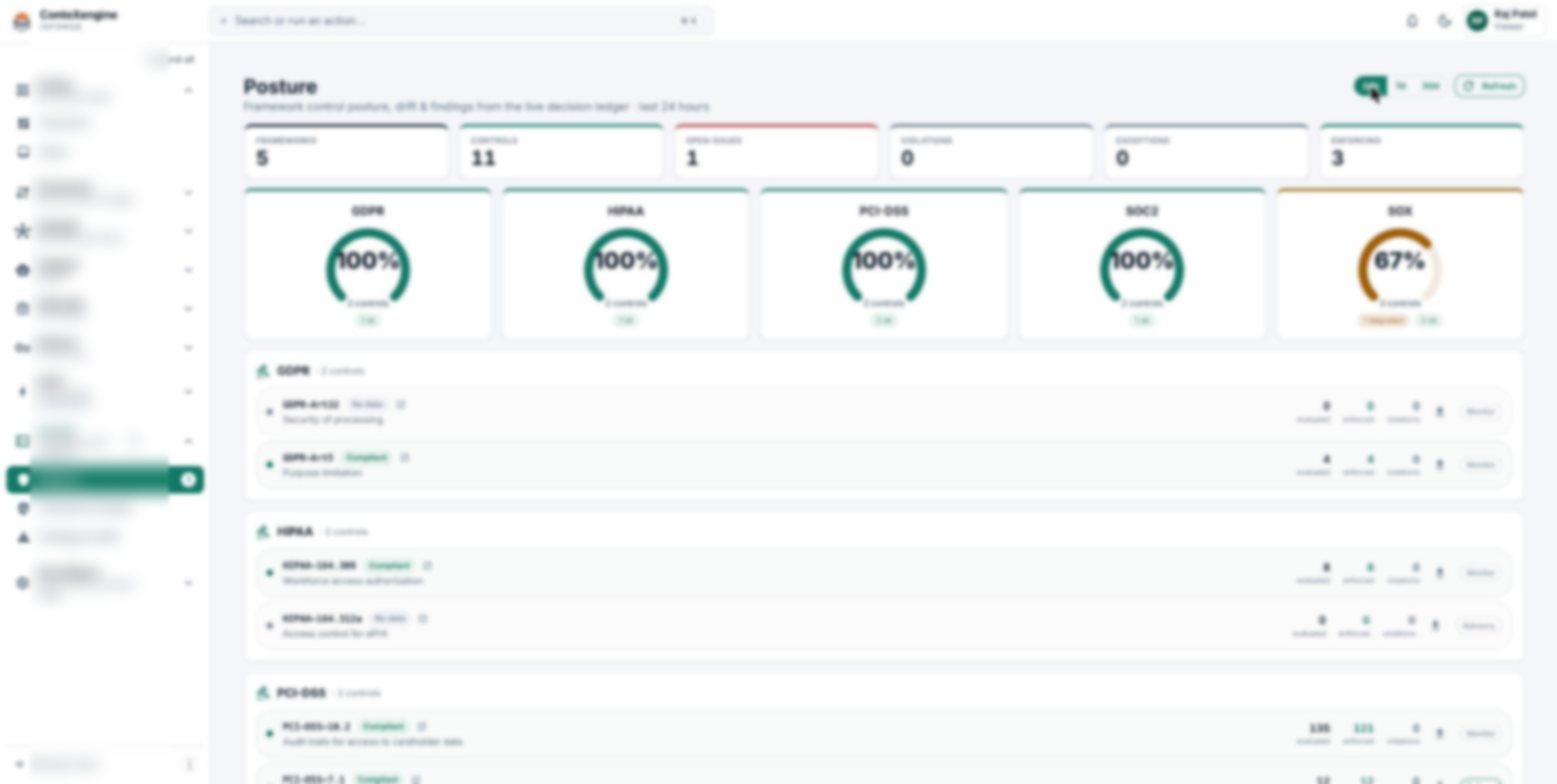
Three things, every day.
Maps decisions to the frameworks you answer to (SOX, PCI DSS, HIPAA, GDPR, SOC 2) and computes posture continuously.
Shows each control: evaluated, enforced, violations, exceptions and who accepted them.
Exports evidence packs that are exactly what the engine computed, with policy versions stamped on every decision.
From signal to decision.
See it decide.
Questions we get asked.
Does this replace our GRC tool?
No. It feeds it with decision-level evidence instead of attestations.
Which frameworks are supported?
SOX, PCI DSS, HIPAA, GDPR and SOC 2 ship as templates; framework scope is configurable.
How current is the evidence?
As current as the last decision. Posture, rollup and export are the same rows.
Can an auditor replay a decision?
Each record keeps the signals, scores and versions in force, so a decision can be checked again later against exactly what was true.