Platform
One graph. Every identity. Five capabilities.
ConteXengine sits above the tools you already run and decides every access call from context. It replaces no directory, vault or governance platform; it is the layer in the middle that none of them is.
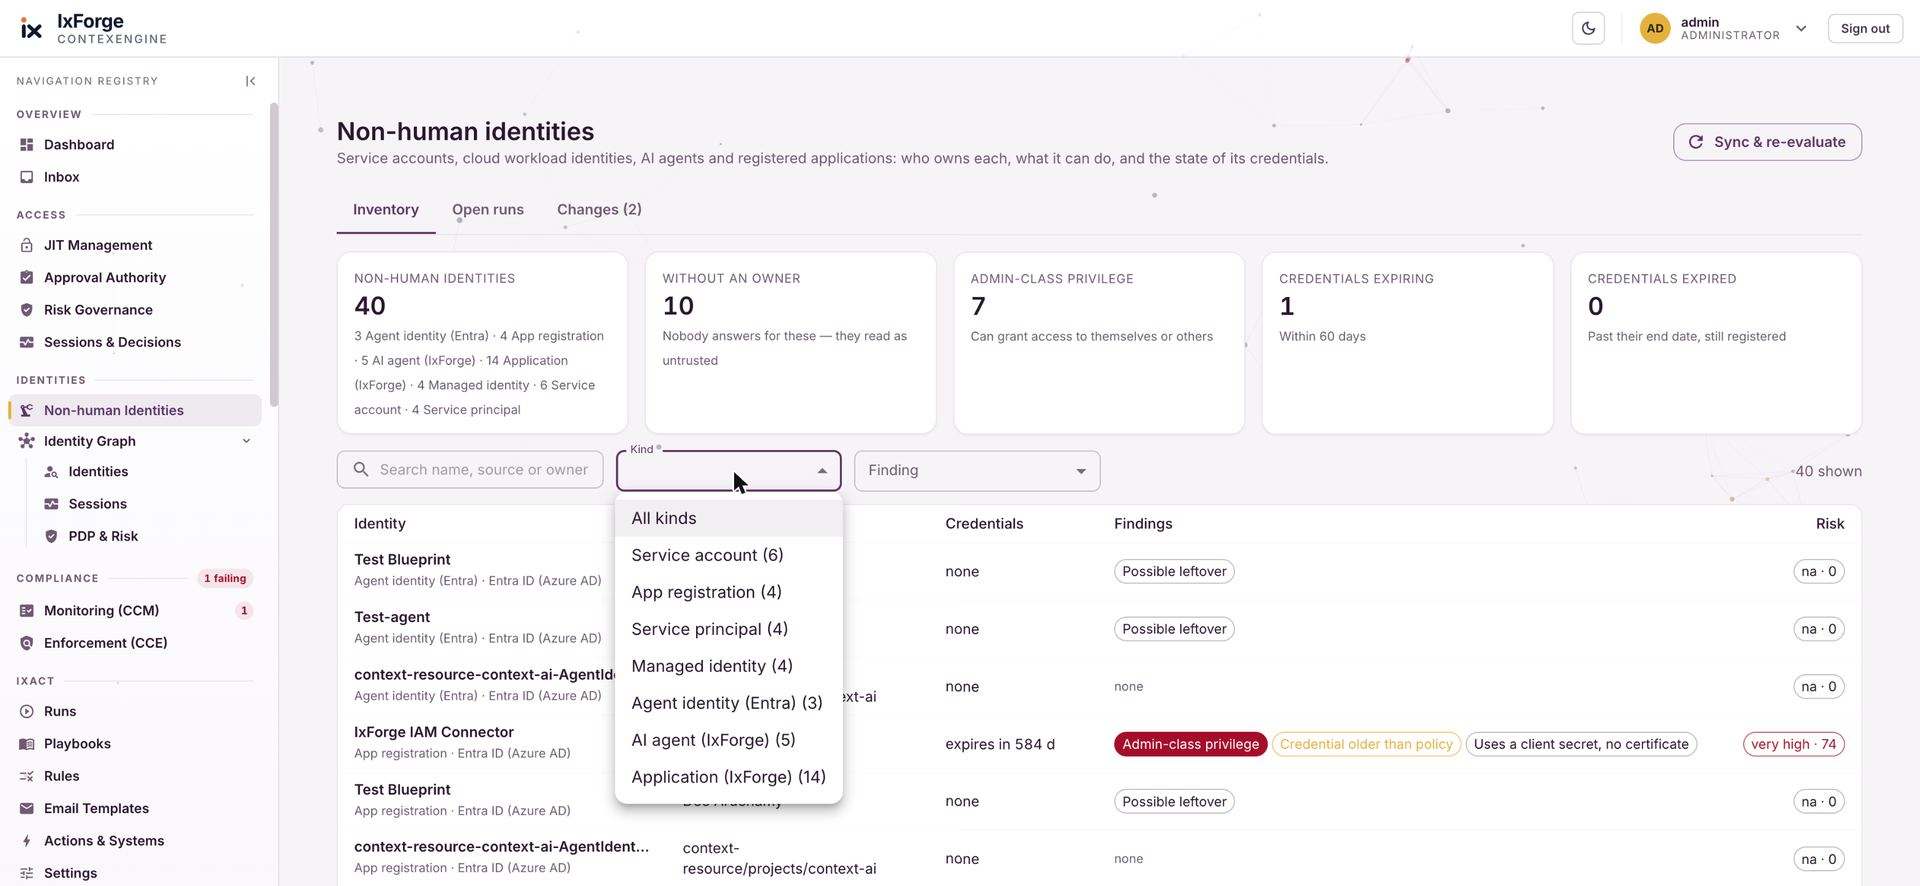
Find
Every identity, from the signals already in your estate.
ConteXengine reads your directory, cloud IAM, data platforms, pipelines and logs and builds one graph of who holds what — people, service accounts, keys, applications and AI agents — with an owner, a reach and the evidence behind each one. Nothing is typed in; nothing is guessed.
- People, machines and agents in one inventory, with owners
- Blast radius computed per identity, not estimated
- Sources that stop delivering stay visibly dark
Score
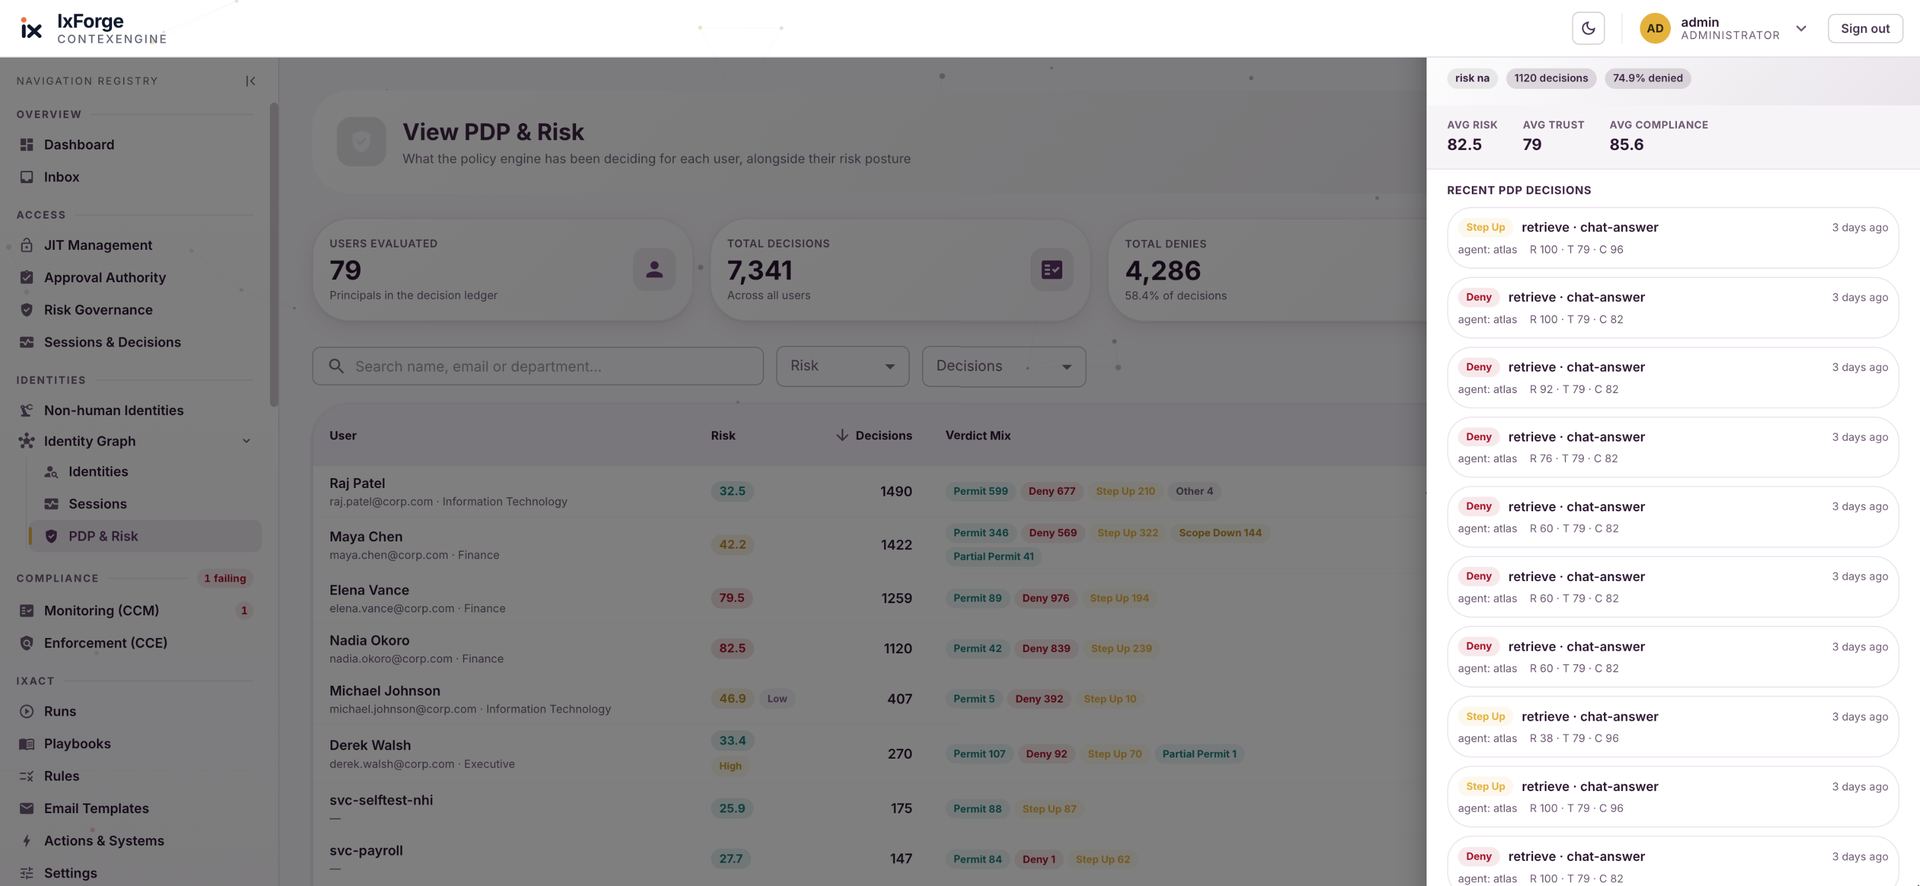
One score for a person, a key and an agent alike.
Risk, compliance and trust are computed on a single published contract from live evidence — credential age, attached policies, last use, device, network, separation of duties. The same bands apply whether the identity is a finance analyst, a payroll service account or a copilot.
- Risk, trust and compliance scores with the reason behind each
- The same contract for every population
- Scores move the verdict, in real time
Govern
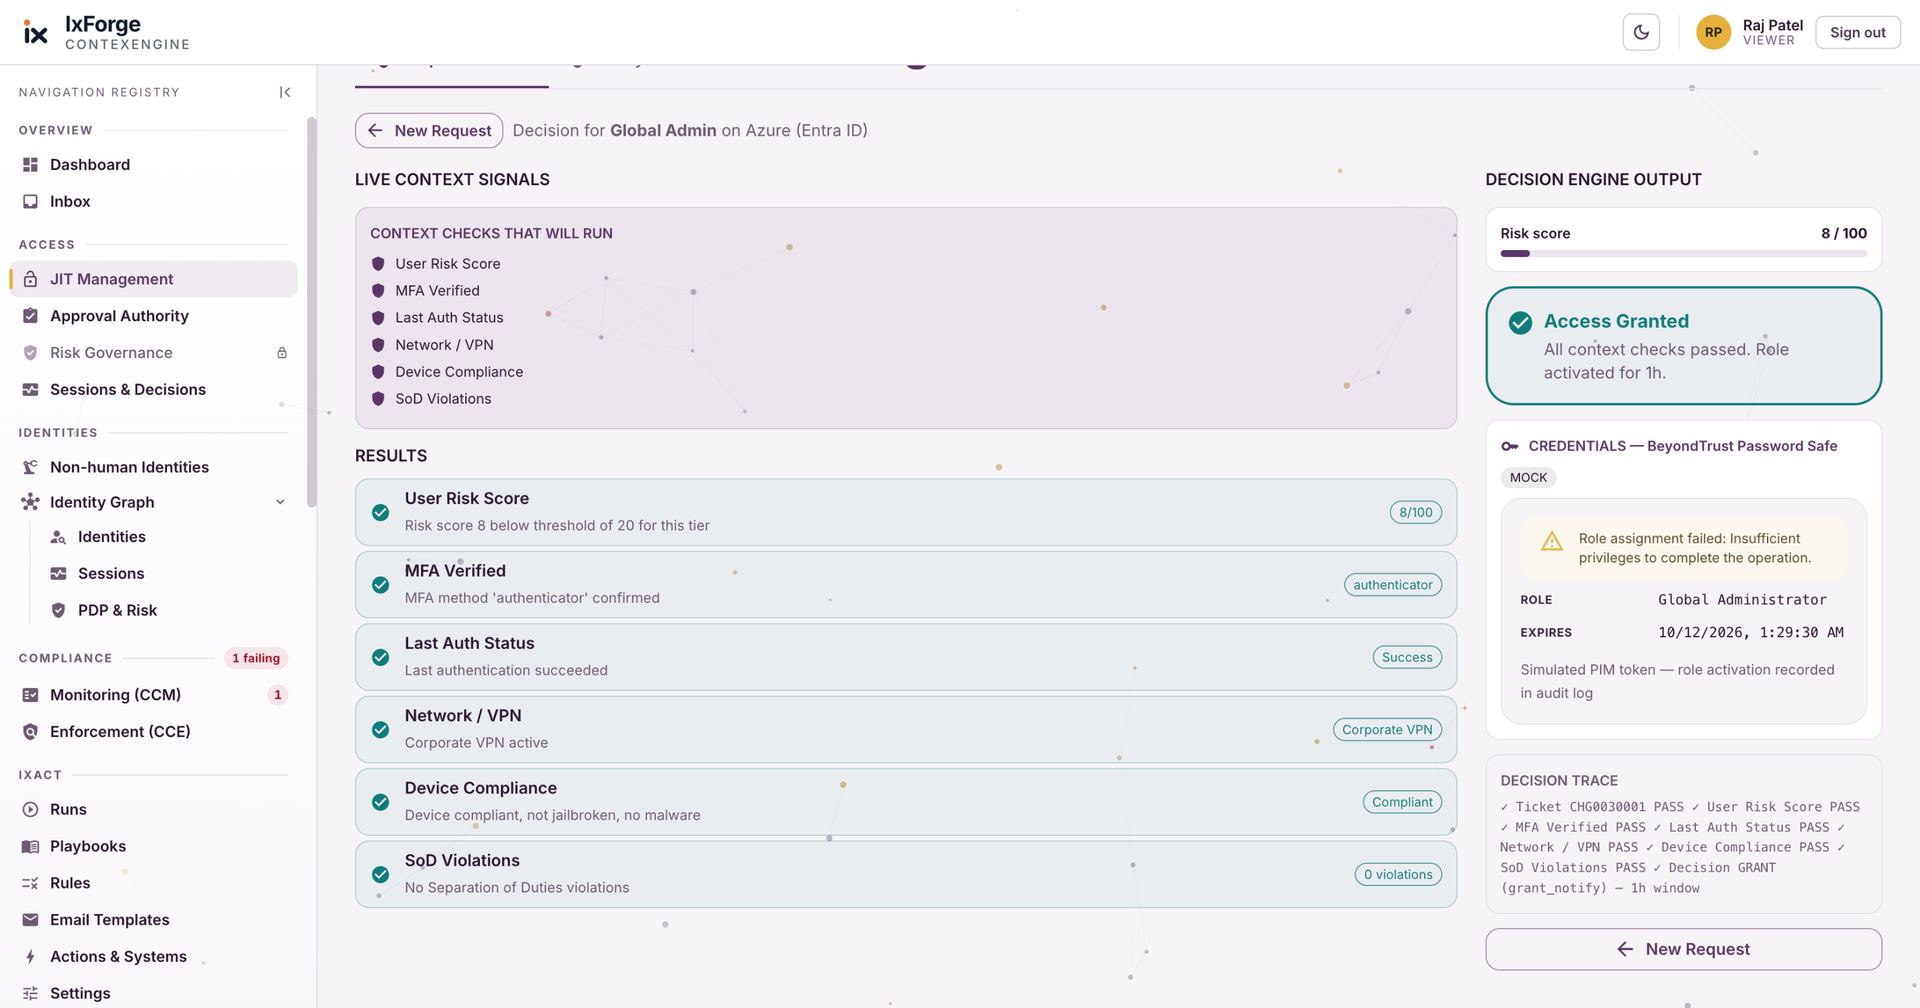
Standing privilege to zero, without a policy project.
Eligibility is computed per request from the graph and six live signals, so there is no standing role to find and no timer to maintain. Static keys become just-in-time roles in one governed run; the finding closes instead of ageing in a ticket.
- Just-in-time for humans, agents and machine identities
- Static key to JIT role in one governed run
- Approval, window and scope set by context
Grant
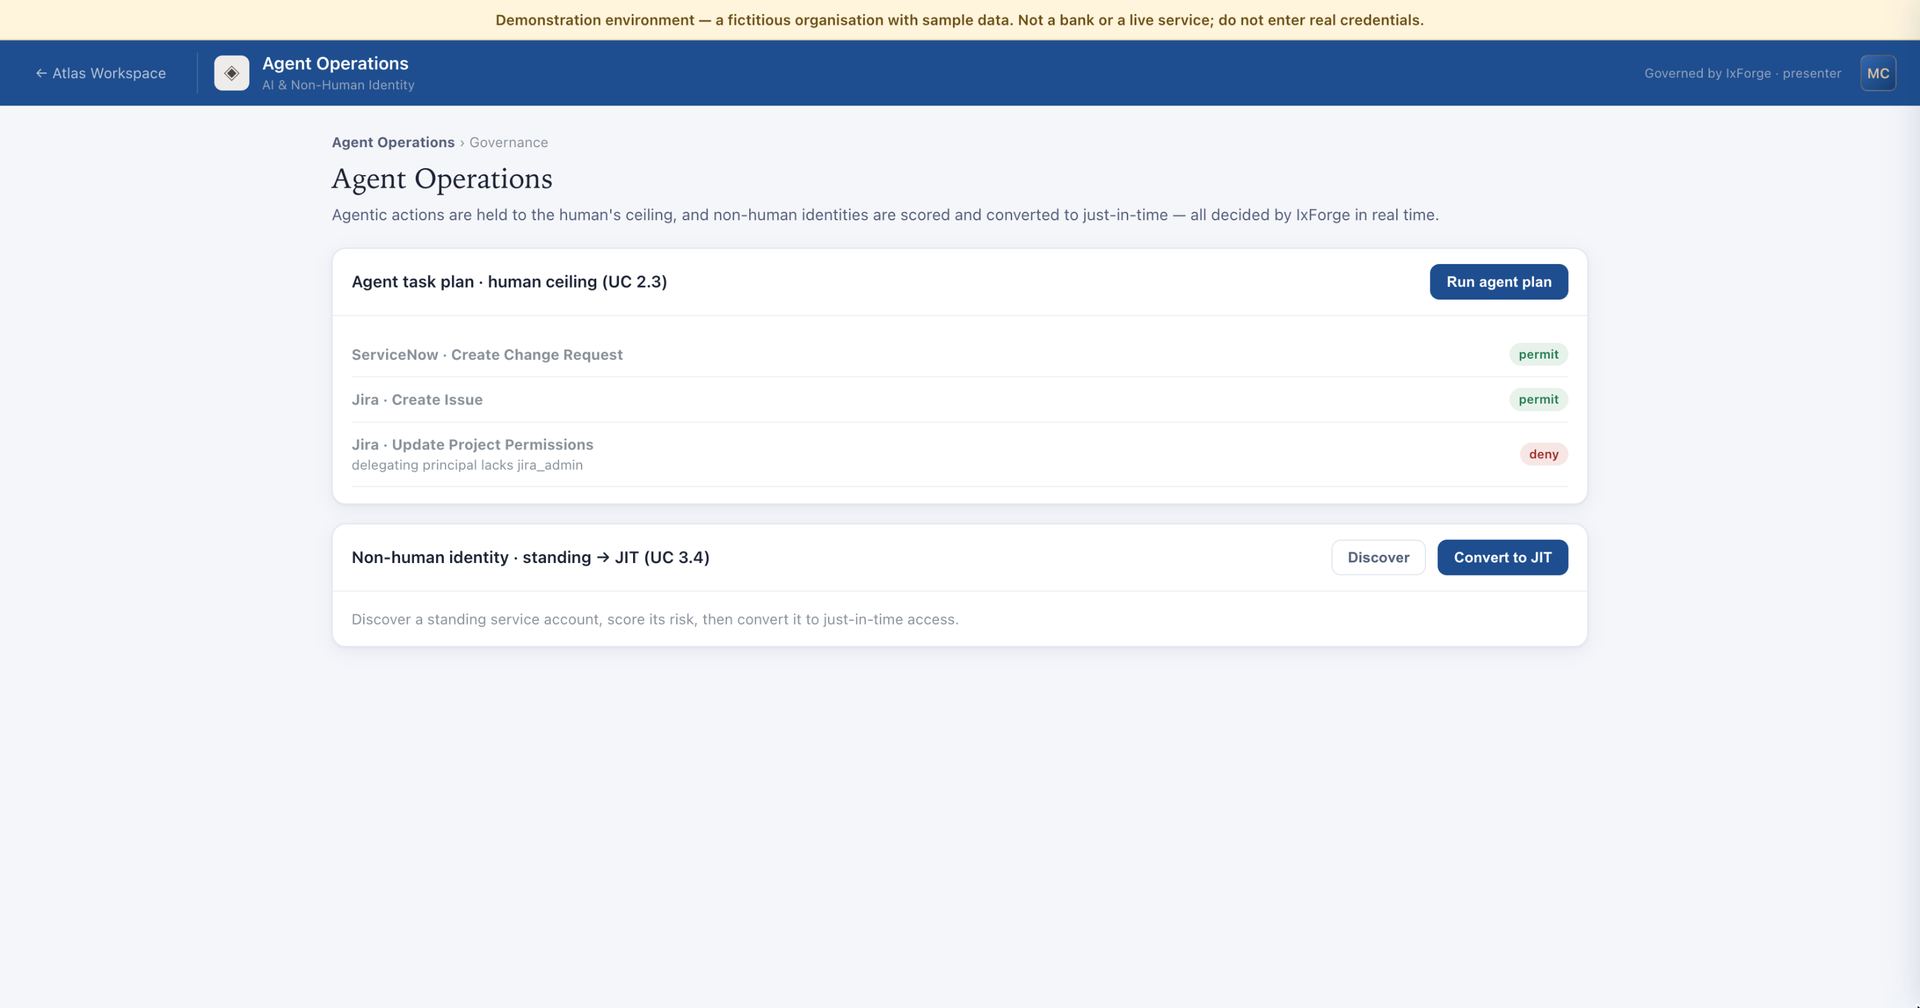
A verdict per call — bounded by the human, scoped to the data.
Agents inherit within the ceiling of the person they work for, and authority only shrinks as it passes down a chain. Copilots retrieve per asker, per chunk, with classification and lineage attached before anything enters an index. The unmapped element stays dark and fails closed.
- Delegation bounded at every hop
- Retrieval decided per chunk, per asker
- Contain in seconds across connected apps
Prove
The audit was done the moment the decision was made.
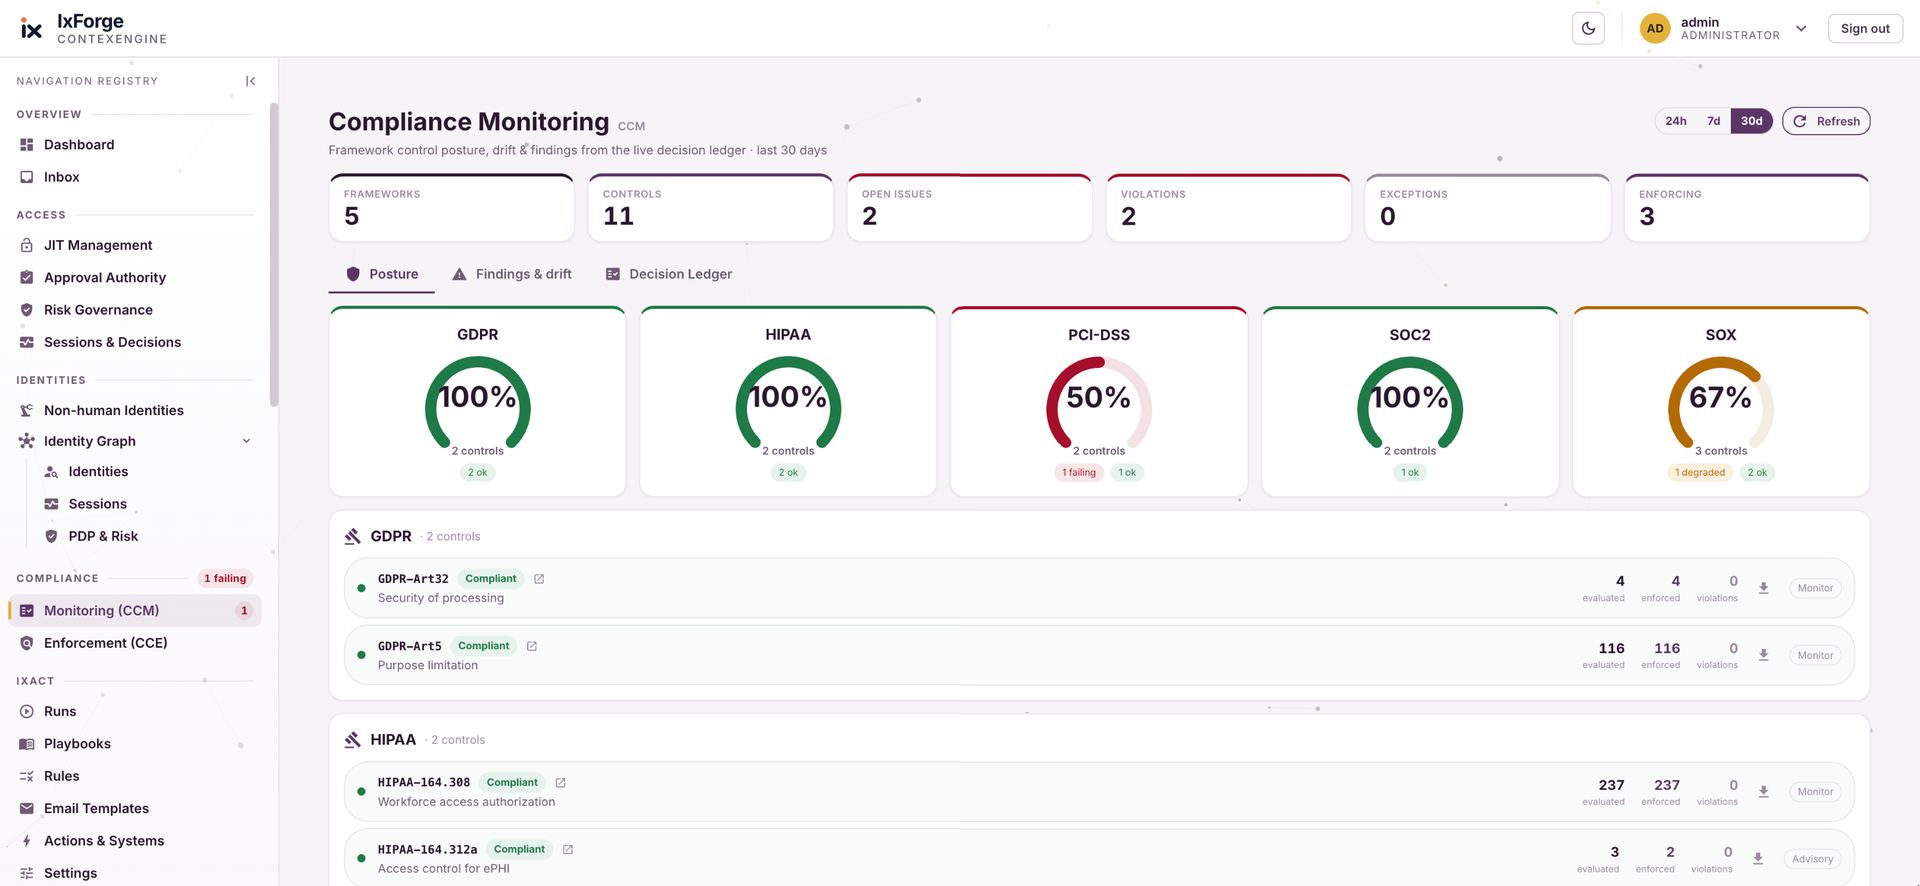
Every verdict carries its causal chain — the path walked, the scores, the signals that fired, the policy versions in force. Dashboard, rollup and export are the same rows. Pick a framework and export the evidence pack.
- One ledger behind every screen
- Policy versions stamped on every decision
- Evidence packs per framework, on demand
What’s live today
ConteXengine · IxAct · IxKinect
ConteXengine began as the decision brain. The same engine now discovers every identity, retires standing privilege, governs AI agents and proves every decision. Everything below is labelled for what it is today.
Discover every identity
Every human, service account, key, token, workload and AI agent, who owns it, and what it can reach.
- Non-human identity discovery and inventoryLive today
- Credential age, expiry and ownership findingsLive today
- Exposed secrets and what they could reachLive today
- Effective access and blast radiusLive today
- Dormant, orphaned and over-broad accessLive today
- AI agents registered as identities with ownersLive today
Decide every request
A verdict for every request from every actor, computed from live context.
- Five verdicts: Permit, Scope-Down, Step-Up, Defer, DenyLive today
- Computed risk, compliance and trust scoresLive today
- Runtime graph reasoningLive today
- Policy Simulator: test an intent before anyone asksLive today
- Behavior and usage intelligenceIn build
Retire standing privilege
Access granted when context justifies it, and removed when it doesn’t.
- Just-in-time, scoped, time-boxed grantsLive today
- Change-ticket validation before eligibilityLive today
- Re-decision and revocation mid-sessionLive today
- Zero standing privilege for service accounts and workloadsLive today
- Static key to just-in-time role in one governed runLive today
Govern AI agents
Agents act on delegated authority that can only shrink, never grow.
- No agent exceeds the human it representsLive today
- Delegation attenuated hop by hopLive today
- Agent session risk and auto-quarantineLive today
- Agent owner consoleRolling out
- Agent front door for MCP and agent-to-agent callsIn build
- Intent-to-action alignmentIn build
Contain in seconds · IxAct
Pull access back at the scope the situation needs, everywhere it applies — and turn findings into actions.
- Risk-tiered ceilings and containmentLive today
- Seventeen built-in actions that run on every connected systemLive today
- Revoke sessions, disable identity, remove access, rotate credentialLive today
- Playbooks and governed runs with two-person approvalLive today
- Shared-signals hub (CAEP) to identity providers and appsRolling out
- Kill switch at every scopeIn build
Connect · IxKinect
The connector fabric: read every source, act on every system that allows it.
- Directories, identity providers and cloud IAMLive today
- Data platforms, pipelines and cataloguesLive today
- ITSM, SIEM and logs as signalsLive today
- Source coverage shown honestly: delivering, partial, not yet builtLive today
- Write-back enabled per system by an administratorLive today
Prove everything
Evidence an auditor can read, mapped to the frameworks you answer to.
- Explainable provenance for every decisionLive today
- SOX, HIPAA, PCI-DSS, GDPR and SOC 2 context modelsLive today
- Evidence pack export per frameworkLive today
- Tamper-evident evidence and platform self-protectionIn build
Capabilities marked In build are on the roadmap and not yet generally available.
Give every identity exactly the authority its risk earns. Take it back the instant that risk changes. Prove both.
Runs in your environment
Deployed inside your boundary, including isolated networks. Your data stays where it is.
No AI in the decision path
Models help us build and tune. Every live verdict is deterministic and replayable.
Built and run with you
A build partner connects your estate, then a 24×7 global command center runs it with you.
Patent pending
A new approach to runtime authorization for the agentic enterprise.